
Cases · 2026-10-12 · 4 min read
Ledger wallets drained after *physical implants* found in devices
Hardware wallet maker Ledger reports $93 million stolen after tampered devices reached customers through a Southeast Asian reseller, raising questions about supply-chain integrity in products sold as secure.

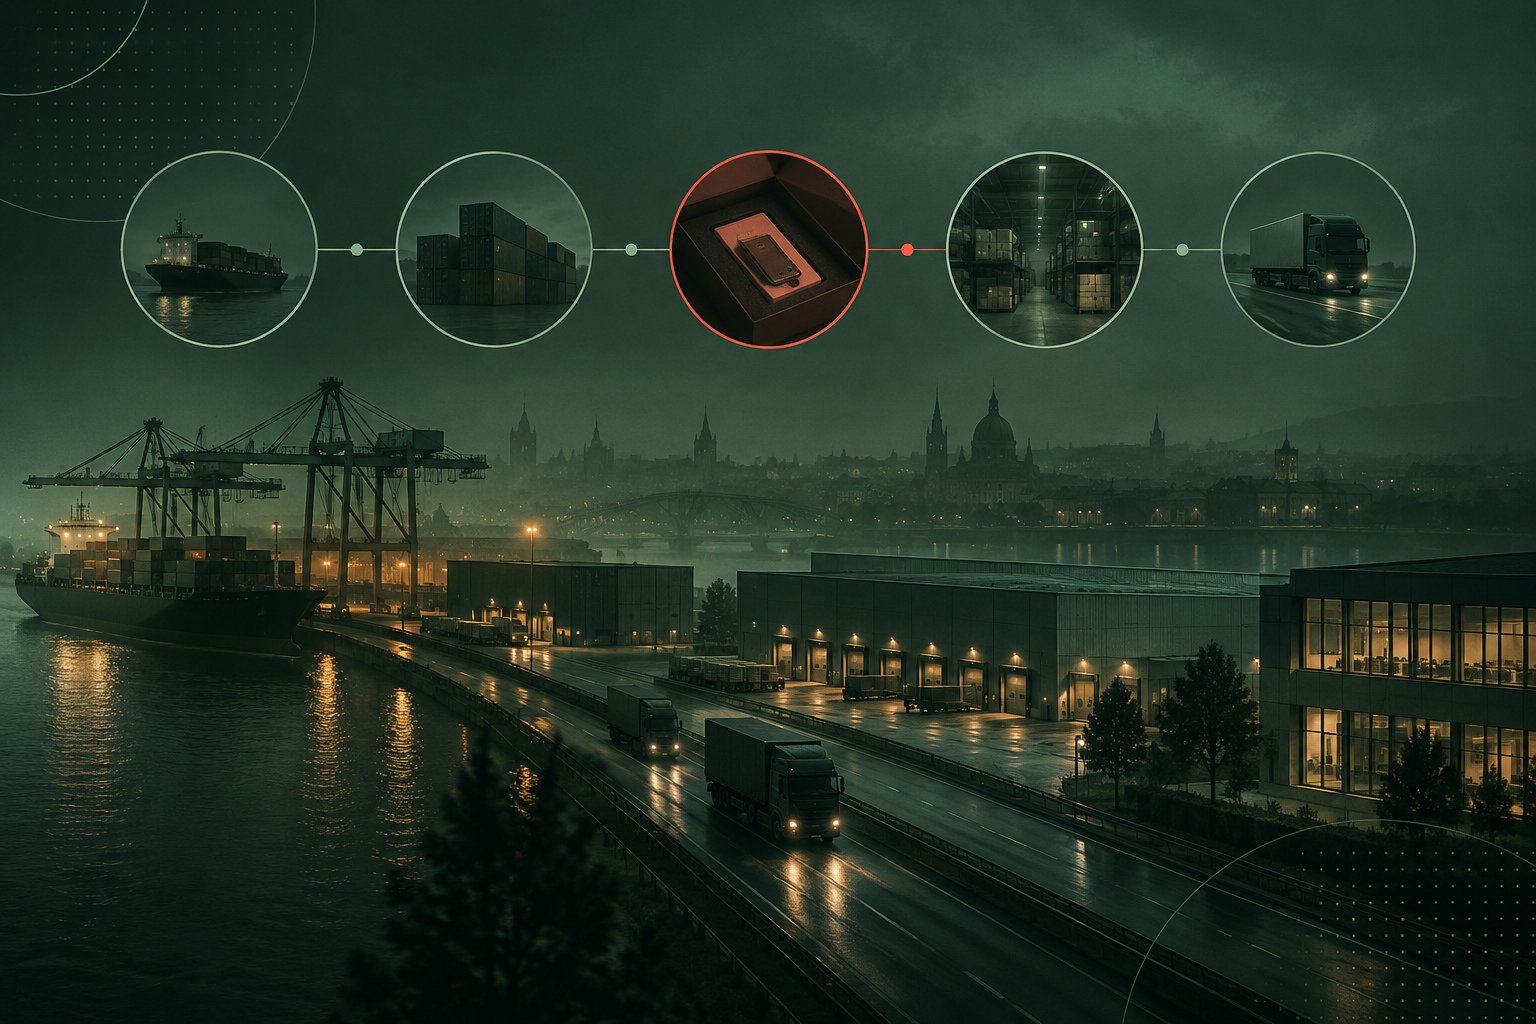
A hardware implant, not a software hack
Hardware wallets are meant to be the safe option. They keep your private keys offline, away from malware and remote attacks. Ledger is one of the best-known makers. So when $93 million in cryptocurrency disappeared from Ledger devices in October 2026, people assumed it was a software breach.
It wasn't. Ledger found physical implants in devices sold through CryptoBilis, a reseller in Southeast Asia. Every confirmed draining incident traced back to wallets distributed through that channel [1].
Think of it like this: you buy what looks like a new toaster, shrink-wrapped and boxed. You take it home, plug it in and make breakfast. What you don't see is the extra chip someone soldered inside the heating element at a warehouse along the way. The toaster works fine, but it's also quietly recording everything you do.
What the implant did
The implants were discovered during Ledger's investigation after reports of funds draining from wallets that had been set up and used normally. The devices functioned as expected, displayed Ledger's interface and passed the company's basic integrity checks when customers set them up [1].
The implant sat between the legitimate hardware and the user, capturing private keys or seed phrases as they were generated or entered. Once it had that information, draining the wallet was straightforward.
Ledger has confirmed that devices sold directly from the company, or through verified channels outside CryptoBilis, were not affected. The problem was contained to one distribution path, but that was enough [1].
The supply-chain question
This is a supply-chain attack, and it's harder to defend against than a software vulnerability. Ledger can patch software remotely. It can't remotely verify what's inside a device that left the factory intact but was opened and modified somewhere between the warehouse and the customer.
The reseller model relies on trust. Manufacturers send devices to partners, who handle storage, packaging and delivery. Most of the time it works. When it doesn't, the manufacturer finds out the same way everyone else does: when customers report losses.
Ledger says it has suspended the relationship with CryptoBilis and is reviewing its distribution practices [1]. That matters for future sales, but it doesn't help the people whose funds are already gone.
Why hardware felt safer
People choose hardware wallets precisely because they're supposed to be isolated. No internet connection, no background processes, no way for remote attackers to reach the keys. The advice has been consistent for years: if you're holding significant value, use a hardware wallet.
That advice assumed the hardware itself was trustworthy. Most security models do. A physical implant breaks that assumption, and there's no software update that fixes it.
It's not that hardware wallets have suddenly become unsafe. Ledger devices sold through legitimate channels remain one of the more secure options for holding cryptocurrency. But the case shows that "more secure" is not the same as "impossible to compromise", especially when the attack happens before the device reaches you.
What this means for you
If you use a hardware wallet, check where you bought it. Devices purchased directly from the manufacturer, or from well-known retailers with documented supply chains, are far less likely to have been tampered with.
If you bought a Ledger device through CryptoBilis, or any reseller you're not certain about, treat it as compromised. Move your funds to a new wallet, with a new seed phrase, generated on a device you trust.
For anyone selling hardware security products, the question is how you verify that what reaches the customer is what left your factory. Tamper-evident packaging helps, but it's not enough if someone with the right tools can reseal it. Serial numbers and integrity checks at setup catch some attacks, but they didn't catch this one.
The harder question is this: if a device is tampered with in your distribution chain, how would you know, and how quickly?
Sealing won't stop a hardware implant, but it changes the question
A digital witness doesn't protect the hardware. It can't detect an implant, and it won't stop funds from draining if the device is compromised. What it does is make the supply chain visible after the fact.
Here, the thing to seal is each distribution event: which device left the factory, when, to which partner, and which devices that partner reported as delivered. Sealing takes a fingerprint of each record, not the record itself, so it doesn't require sharing customer data. The manufacturer keeps the records, and the seal makes them checkable.
If questions come up later, the sealed records show where a device went and when. They don't prove the device wasn't tampered with, but they show who had it and for how long, which narrows the investigation.
For customers, a sealed record of the device's origin and path—checked against the manufacturer's records before first use—gives one more data point. It doesn't replace tamper-evident packaging or integrity checks, but it adds a layer that's harder to fake quietly.
You can seal distribution records through WitniumChain using the REST API or SDK. The content stays with you, the fingerprint is sealed and anyone you share the record with can check it. The first 2,000 witnesses a month are free. Read the docs.
How it would work
- Seal each device's shipment record when it leaves the factory and again when the reseller confirms receipt
- Seal the reseller's delivery confirmation when the customer receives the device
- Before first use, the customer checks the sealed records against the manufacturer's database to confirm the device's path
What to watch
Ledger has not yet published a full technical report on how the implants were discovered or exactly how they functioned. Watch for that, and for any changes in how hardware wallet makers verify their distribution channels.
Broader supply-chain security will get more attention under the Cyber Resilience Act, which applies from 11 December 2027 for products with digital elements. Manufacturers will have to show they know what happens between the factory and the customer [2].
For cryptocurrency holders, the short-term advice is simple: verify where your hardware wallet came from, and if there's any doubt, move your funds to a new device with a new seed phrase.
Sources
- [1]Ledger wallets compromised via hardware implant, Help Net Security, 2026-10-12
- [2]Regulation (EU) 2024/2847 on cybersecurity requirements for products with digital elements, EUR-Lex, 2024-10-10